
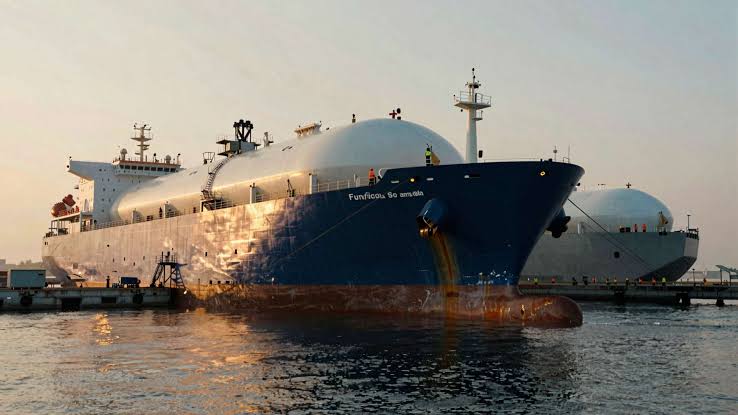
The U.S. Coast Guard and FBI are jointly investigating suspected cyberattacks on two oil tankers that were bound for the United States last month.
Both vessels were boarded by American authorities following indications that their onboard networks had been compromised by foreign cyber actors operating with hostile intent.
On August 21, a foreign-flagged commercial vessel in the Gulf of Mexico was boarded by a highly specialized team of Coast Guard law enforcement officers, cyber protection members, and FBI cyber personnel.
A joint statement from both agencies confirmed that “the measures were designed to ensure integrity of the vessel’s operational and information technology systems following indications that the vessel’s network were compromised by foreign cyber actors.”
A second tanker that sustained a cyberattack was subsequently boarded by U.S. officials on August 24 to conduct a comparable systems assessment and security review.
Investigators are actively examining the possibility that Iran, or another actor seeking to exploit ongoing tensions between Tehran and Washington, was responsible for the attacks.
The joint Coast Guard and FBI statement noted that “currently, there are no reports of operational disruptions, vessel instability, physical danger to crews, or environmental impacts” stemming from either incident.
One of the vessels involved has been identified as the VL PROSPERITY, a Liberian-flagged supertanker with a capacity of 2.3 million barrels of crude oil.
The VL PROSPERITY was sailing from Egypt’s Sidi Kerir port toward a U.S. port when it was targeted by a major cyberattack in the Strait of Gibraltar on August 7, 2026, leaving it without communications for 30 hours.
According to a crew member aboard the vessel, attackers infiltrated engine-room systems, reduced engine cooling flow, increased engine speed, and disabled fuel and engine-oil tank controls during the breach.
The sophistication of the attack on the VL PROSPERITY points to a well-resourced threat actor with specific knowledge of maritime operational technology systems and their vulnerabilities.
No group has yet claimed responsibility for either attack, and both investigations remain active as federal authorities work to attribute the incidents and assess the broader threat to maritime infrastructure.
